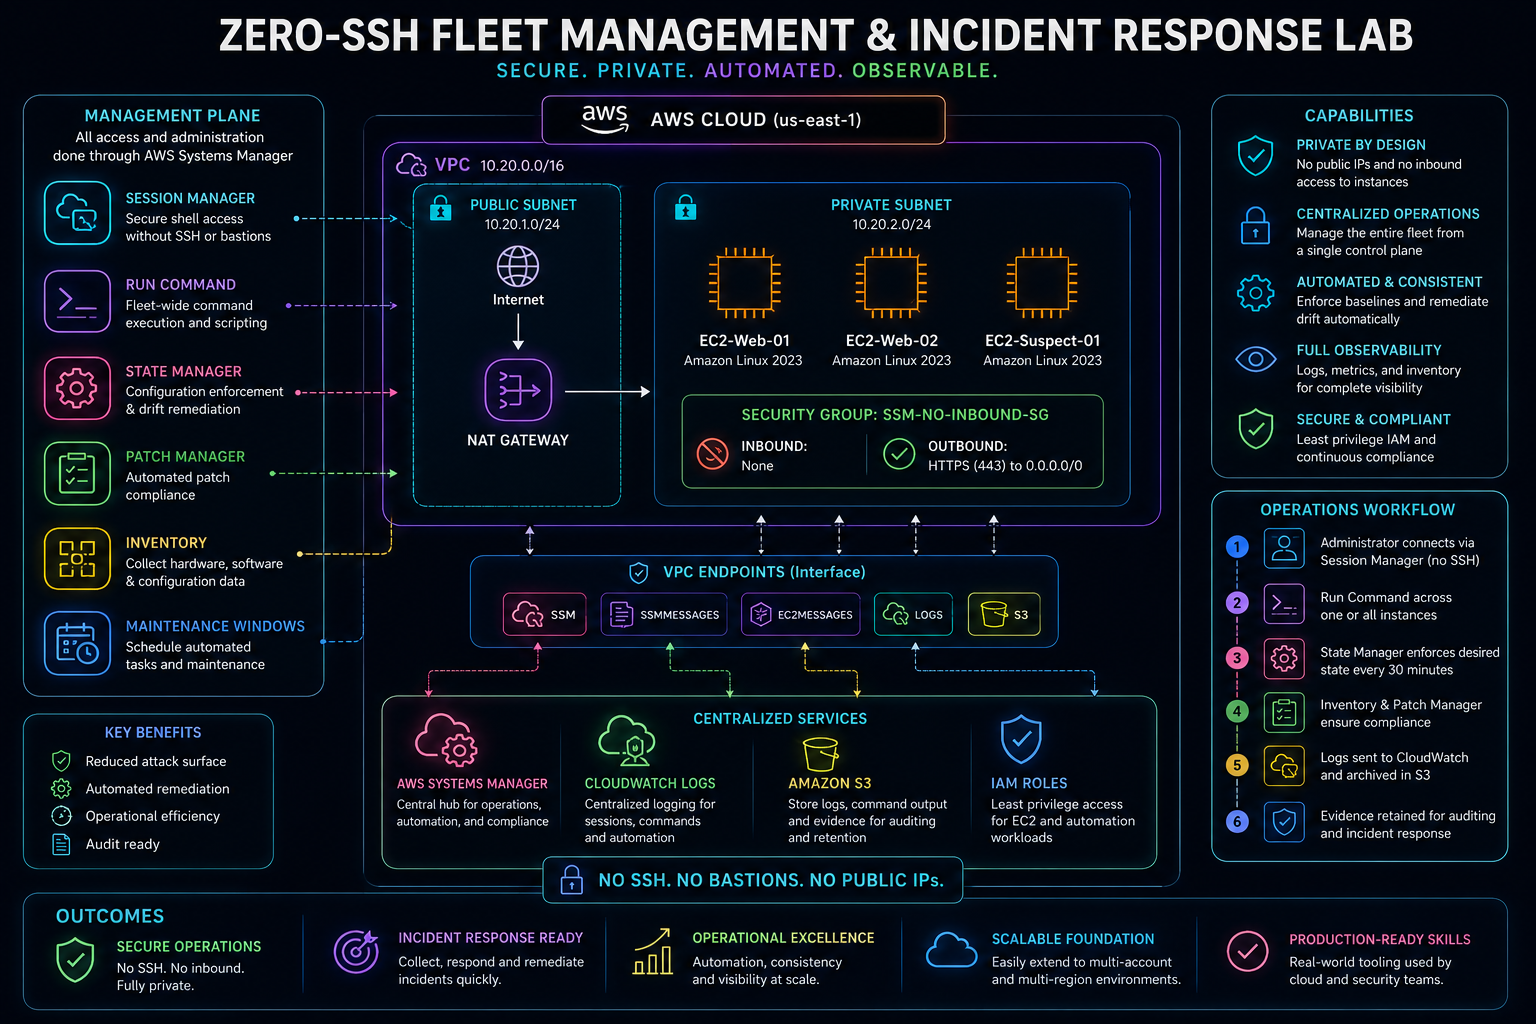
Designed and implemented a private AWS EC2 environment managed entirely through AWS Systems Manager without exposing inbound SSH access or public IP addresses. Leveraged Session Manager, Run Command, State Manager, CloudWatch Logs, and centralized S3 logging to perform secure fleet-wide administration, configuration enforcement, automated remediation, and operational auditing across multiple Linux instances.